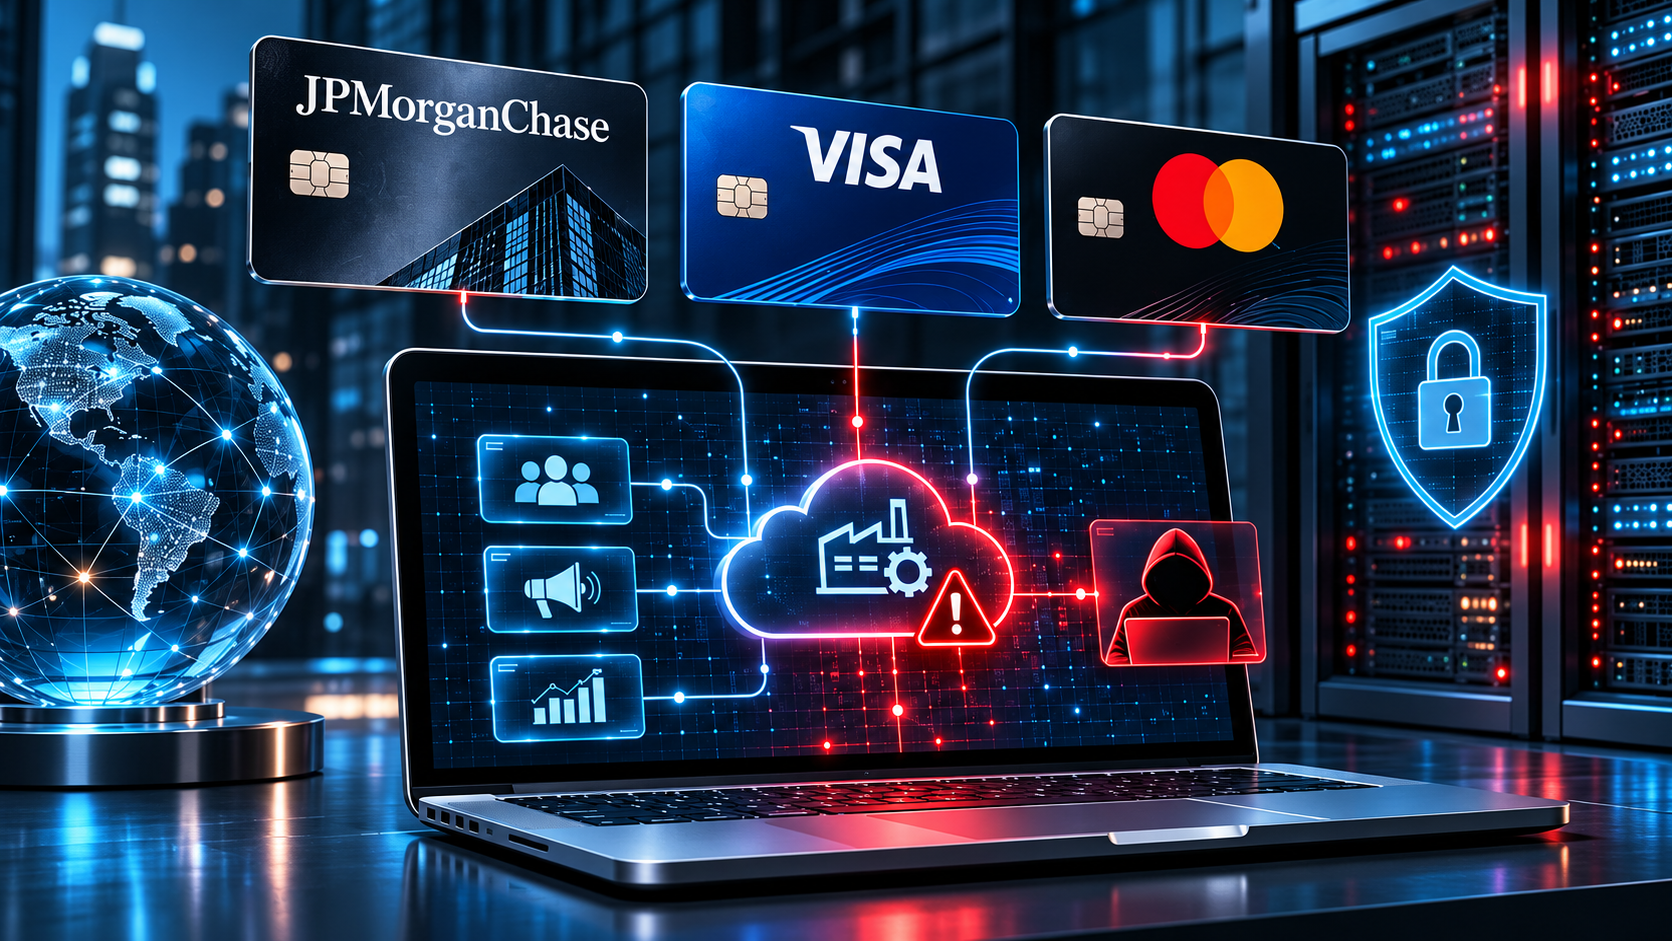
New York: Customer information linked to JPMorgan Chase, Visa, and Mastercard were exposed in a cyberattack targeting third party service providers, with hackers publishing data allegedly belonging to thousands of customers.
The three financial companies confirmed the incidents on November 19, but said their internal payment systems were not compromised.
JPMorgan, the largest US bank, said attackers appeared to access marketing information held by outside vendors, including customer names and email addresses.
The bank said affected customers would be contacted directly and offered assistance, including complimentary credit monitoring.
More than 16,000 customer email addresses exposed
A Reuters examination of material published by the attackers identified more than 16,000 apparent JPMorgan customer email addresses and 124 bank employee email addresses.
Some records also contained telephone numbers and postal codes.
However, reports said it could not independently verify the authenticity of the published information.
The bank did not comment on the specific files released by the hackers.
The affected information is believed to come from external companies that manage marketing and customer engagement services.
JPMorgan said the incident did not affect its banking operations or payment services.
Visa and Mastercard confirm vendor breaches
Visa said the reported breach involved a third-party service provider operating in the Asia-Pacific region.
The company maintained that its own systems were not compromised and that sensitive payment information, including card numbers, were not exposed.
According to Reuters, the purported Visa data included customer email addresses, telephone numbers and marketing records from several Asia-Pacific markets.
These included Hong Kong, Taiwan, South Korea, Japan, the Philippines, Singapore, Malaysia and Australia.
Mastercard separately confirmed that a service provider experienced a security incident.
The company said a limited number of email addresses belonging to cardholders enrolled in a particular benefits programme were exposed.
It added that the incident did not affect its global payment network or customers’ ability to use their cards.
Hacking group claims responsibility
A cyber extortion group calling itself n0n claimed on November 16 that it obtained customer engagement records linked to JPMorgan.
The group subsequently published similar claims involving Visa and Mastercard.
According to cybersecurity researchers, the group alleged that the stolen material contained hundreds of thousands of marketing interactions involving tens of thousands of customer email addresses.
Cybersecurity firm SOCRadar said the group published documents supporting its allegations but that their authenticity was not independently established.
The group reportedly emerged in September 2026 and since claimed responsibility for attacks involving nearly 200 organisations.
Bank says earlier service outage was unrelated
JPMorgan also clarified that the cyberattack was unrelated to a technical disruption affecting its banking services earlier in the week.
That disruption was attributed to a software problem that temporarily affected transaction processing at several financial institutions.
The bank maintained that customer accounts and payment operations were not affected by the vendor breach.
The incident renewed scrutiny of how banks and payment companies protect customer information shared with external service providers.
Although the companies ruled out the exposure of payment card details, the investigation continues into the extent of the customer information accessed through the affected vendors.